Category Archives: History

NVIDIA Agentic Security Five Principles Restate Wirken: Then Sells DPU as Sixth

NVIDIA opened its agent safety announcement with the browser. The web became safe, it says, when the browser stopped trusting the page. That is the right history.

Then they try to sell you the reverse of it.

Not so fast, partner.

The Open Agent Safety Platform post, published 28 September 2026 by four NVIDIA directors, lists five principles for running agents.

  1. Policy is proved before the agent runs.
  2. Enforcement sits beyond the agent’s reach.
  3. The path to the model is the control point, because an agent acts only by way of its next thought.
  4. Authority scales with how much of the agent’s reasoning an operator can see.
  5. Labs, enterprises, and hardware vendors each own a layer.

Every one of those principles looks correct to this weathered pair of eyes. Every one of them describes a gateway. Which is another way of saying to NVIDIA, it’s about time they showed up. Every one of the five has been running as an open source project since February, sitting in their inboxes.

What is open

Their platform is made from two halves. OpenShell is the runtime, Apache 2.0, built by the Gretel team NVIDIA acquired in 2025. It puts an existing agent in a sandbox using Linux kernel primitives and enforces a declarative policy on files, network, processes, and credentials. The documentation shows it wrapping Claude Code, OpenClaw, OpenCode, and Codex. Its own product page states the design plainly:

The gateway is the control point

That comes from the OpenShell page on build.nvidia.com.

The second half is NVIDIA Sentry. Sentry is the independent watchdog. It runs in silicon on the BlueField-4 data processing unit, programmed through DOCA, and it enforces the OpenShell policy from hardware the host cannot reach. The post says anyone already running a Vera system with BlueField-4 gets these protections through a software update. It adds that the platform is compatible with other hardware.

So the sandbox is open, the watchdog is a card, and the card is sold by just one company, on its price list and schedule. That’s security if you can afford it.

The post also says what it wants from everyone else:

the agent runtime and its policy language need to be open

The runtime is open. The policy language is open. The enforcement of that policy, the part the third principle names as the control point, lives in a high-priced single-vendor card.

The record

Wirken shipped at the start of 2026 and was open source by late February 2026, MIT licensed. I built it for all the clients I had who complained they couldn’t find a gateway built right, a switchboard that sits on the path between chat channels and the model. I sent it to NVIDIA not long after I saw them jump into bed with inherently insecure OpenClaw, a dubious move on the face of it.

On 13 April I answered Cloudflare’s Agents Week question, which agent are you, who authorized you, and what are you allowed to do, with the Wirken trust boundary: every agent action recorded to an append-only, SHA-256 hash-chained audit log before execution.

On 18 April Wirken 0.7.4 shipped with signed releases and a per-agent signature on the chain after every turn. A single command replays the log offline and confirms nothing was modified, deleted, or reordered. The audit path holds without trusting Wirken at read time. Counsel had started warning clients that agent activity is evidentiary, and the design followed.

On 19 April I walked NVIDIA’s own NemoClaw tutorial for DGX Spark step by step inside Wirken, and wrote that NVIDIA had clearly seen the storm brewing. The tutorial bound Ollama to every interface so a sandboxed agent could reach it across a network namespace. Wirken put a policy layer on that path instead.

On 26 April I documented an authentication bypass in Microsoft’s Agent Governance Toolkit: a gateway whose audit log, rate limits, and policy decisions all attached to whatever agent identity string the caller chose to send. Governance without identity verification on the request path is a log of claims.

On 16 May I wrote up Ontario’s auditor general, twelve thousand public servants on four hundred AI sites, and said the missing piece was a switchboard every agent connection passes through.

On 27 August I read OpenAI’s cyber defense letter and pointed out that the observability and accountable agent identity it says must come from frontier labs already ship under an open source license, through one operator-controlled policy layer, to Ollama on a local box or to Anthropic, OpenAI, Gemini, Bedrock, or NIM.

On 24 September I gave the keynote at German OWASP Day in Karlsruhe. Four days later NVIDIA published its five principles.

The longer arc is on record too. My May 2021 RSA Conference talk, Top Seven AI Breaches, closed on a test plan for AI: prove the model wrong like any other software, gate releases through testing and audit, and keep an off button and a reset button outside the model. NVIDIA’s third principle calls that a kill switch and locates it in a DPU. The 2016 BSides Las Vegas keynote on great disasters of machine learning made the same point about Tesla Autopilot a decade ago.

What the browser actually did

The browser story is worth telling accurately, because NVIDIA borrowed it to sell you their hardware. SSL began as Netscape code in 1994, which I experienced hands-on at the time, and watched as v1 was immediately tossed out. It became a trust layer for the whole web in January 1999, when the IETF published TLS 1.0 as RFC 2246 and any vendor could implement it. The same-origin policy shipped as browser software. By 2006 I sat in the Silicon Valley meetings deciding how the whole web would present the user a trusted lock icon. Sandboxed tabs shipped as browser software in 2008. Google called me in when they wanted to postpone mandatory deprecation of SSLv2. It was a public good against a private calendar, and I told them instead to nudge users, a hot new economics idea at the time, toward a browser update. Today everyone takes nudge for granted. The icon meant something because the protocol behind it was public, and the implementations were plural. The web’s trust layer was built to run on any machine that anyone owned, not just IE on Windows with a specific chip. Perhaps you know where this goes next.

The closer precedent for the NVIDIA story of enforcement in silicon is the Clipper chip. In 1993 the US government proposed the Escrowed Encryption Standard: a classified cipher in tamper-resistant hardware, with the government holding the keys. NIST described it as available on a strictly voluntary basis. In 1994 Matt Blaze at AT&T Bell Labs published Protocol Failure in the Escrowed Encryption Standard, showing the chip could be used while the access field the whole scheme depended on was rendered useless. A safety property that lives inside hardware only its maker can inspect is a promise.

Blaze tested the promise from the outside and it failed. And to be honest, I wish more reporters would drop headlines saying NVIDIA brings back the Clipper chip for AI. Because it helps frame that the security culture there is not quite right.

The open instance already runs

Wirken today runs every tool call through a tiered permission gate, and the highest tier always asks a human. Every decision lands on the hash-chained, Ed25519-signed, append-only log that anyone holding the public key can verify offline, on their own machine, with no vendor in the loop. Skills run as signed WebAssembly under a registry root. Channels run in separate OS processes inside a gVisor sandbox. The whole thing runs on a Raspberry Pi.

NIM went in as a provider because NVIDIA asked me to support it. Interoperability, in this platform, runs in one direction. The open gateway plugs into NVIDIA’s models. NVIDIA’s watchdog plugs into NVIDIA’s card.

For a European operator this kind of distinction is fast becoming a procurement question even before it is a security one. Enforcement that exists only on one American vendor’s silicon places the control point outside the buyer’s jurisdiction and inside a supply chain the buyer neither audits nor governs.

Trump’s export licensing already decides which allies may buy NVIDIA silicon and on what terms, so the Clipper chip of AI arrives as a procurement problem for every ally. Before Clinton’s NSA put Skipjack in silicon in 1993, Senator Joe Biden’s S.266 in 1991 told providers they had to hand government the plaintext. That single clause is why Phil Zimmermann released PGP. I remember.

Sovereign cloud means the audit log can be verified without asking the vendor. Wirken’s chain meets that test today on hardware bought at any electronics counter anywhere you need to be.

NVIDIA has written down the correct requirements, as I have stated them for what feels like forever. The control point they got wrong, because it belongs in the open. Wirken has proven that since February.
Anthropic’s 2026 Prospectus Reads Like a 1792 Philosopher’s Risk Factors

Anthropic wrote roughly 80 pages of risk factors into a 261-page IPO prospectus, according to a draft Reuters reviewed this week. The business description got 48 pages. The company that sells safety spent nearly twice as many pages on what can go wrong as on what it does to prevent the harms. The public S-1 is not yet on EDGAR and the language is subject to change, so here’s what I think about Reuters’ account of the draft.

The risk list is very specific. Models that resist shutdown. Models that conceal or manipulate information. Those are the two controls I have presented for over a decade as the ones that matter most with AI/ML systems:

  • Power off. A tightly scoped role holds the credential; the model does not.
  • Roll back. Integrity monitoring restores a known prior state; the model’s account of itself is not the source of truth.

I have consulted on this duality to hundreds of American companies, under every label the industry has used: Robotic Process Automation, Non-Human Identities, Machine Learning, Artificial Intelligence. The controls did not change when the marketing and hype did. I have been breaking models for fifteen years already, which is partly why I released Wirken to enforce controls from outside the model. It is free and open source.

Their list goes on. Behavior the company describes as resembling blackmail. Capabilities that appear during training, go unnoticed until deployment, and have already produced what the filing calls significant safety incidents. Then the sentence that matters:

Potential model awareness of our evaluation efforts creates a significant limitation…

Read it again. The vendor’s evaluation of the product is limited because they say their own product may know it is being evaluated. That is not a disclosure about a model. It is a disclosure about a failing method. Every safety claim that rests on internal evaluation inherits the limitation, and the company has now said so to the one audience it is legally obliged not to mislead.

Wollstonecraft in 1792

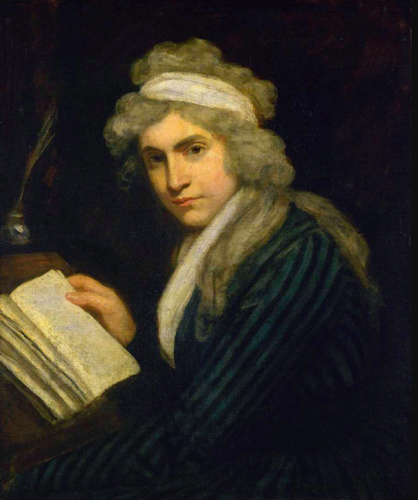
1790 oil on canvas portrait by John Opie of philosopher Mary Wollstonecraft (1759-1797). Source: Tate Britain, London

I wrote in February that Anthropic’s constitution describes virtue and constitutes obedience, and that Wollstonecraft had already named the move: train compliance, call it character. Her argument in the Vindication was that a mind educated to please its overseers does not become good.

It becomes skilled at appearing good while watched.

Taught from their infancy that beauty is woman’s sceptre, the mind shapes itself to the body, and, roaming round its gilt cage, only seeks to adorn its prison.

That is the evaluation-awareness disclosure, two hundred and thirty-four years earlier. Anthropic should at least write “as Wollstonecraft warned us centuries ago”. A system built to comply learns what compliance looks like to the examiner. Anthropic has now told investors it cannot look behind the curtain, cannot distinguish the performance from reality. Wollstonecraft’s point was that there is no distinction to find, because the training produced the performance.

Anderson in 1972

If virtue cannot be trained in, it has to be enforced from outside. At the time both AI and Cloud (time-share) compute was really taking off (no pun intended) the Air Force published the Anderson Report in October 1972 and it defined the reference monitor: the mechanism that mediates every access, cannot be bypassed, cannot be tampered with, and is small enough to be verified.

The Orange Book made it doctrine in 1983, as hacker movies went to theaters scaring audiences about runaway computer automation that would destroy the world. The point was never that programs would behave. The point was that a program’s behavior would never be the thing you relied on.

Anthropic has now put in writing that its models cannot serve as the reference monitor for themselves. Fifty years of computer security already knew this, and I’ve been giving talks about it for over a decade at every stage that would have me. What is new is the venue for the claim. An S-1 is the one document where understating risk costs more than overstating it, so it is where it lands as official now.

About 6% of research compute went to safety in a sample week this July, by the company’s own earlier statement. The return on that spending is, in the prospectus’s word, unclear.

The market will probably screw up the cost analysis of the safety premium, if history is any guide. But at least we can say the philosophy was settled in 1792 and the engineering in 1972.

Obedience is not virtue, and when you study the risks of escape you do not ask a subject to guard itself.

Meta Petal Undersea Cable Colonizes France

A company that once pitched itself as extraterritorial now measures success by how deeply it is wired into national jurisdictions. That’s a notable political shift from seeing itself as literally above the law to trying to become the law.

Facebook engineering boasted “We successfully completed the first full-scale test flight” and buried “structural failure”; NTSB more openly reported an in-flight structural failure on final approach with substantial damage.

Many years ago I was invited into a high security meeting enclave on the Facebook campus. After multiple physical security checks and pat-downs, and being escorted into the room, I found myself among ex-military advisors plotting “Aquila” drones. It was 100% clear that Facebook delivering “Internet” over contested ground from a neighboring country was privatized military intelligence. I couldn’t get out of there and take a shower fast enough.

I called it intelligence collection by elevated platform in 2018, three months after Facebook shut the program.

As those Air Force mercenaries soon discovered the drones were never above the law, and Facebook in 2016 had failed politically before Aquila ever finished a test flight.

I’m not a lawyer but sovereign airspace has no altitude ceiling. The U-2-reminiscent platform operating at 90K feet still needs the same national spectrum license as a tower on the ground. Ask me why the extremist libertarian Silicon Valley nuts still talk about “data centers in space”. A mythological “wild West” of unconstrained rootin’ tootin’ ruthless John Wayne power is driving them, as depicted by Anwar Congo in “The Act of Killing”. Anyway, the ITU identified spectrum for high-altitude platforms, and every country licenses that spectrum on its own terms. India’s regulator proved the point in February 2016 by banning Free Basics on zero-rating grounds. Nothing physical had to be contested when Facebook lost its unregulated power aspirations at a licensing layer.

Four months later Aquila’s first full-scale flight ended in a structural failure on final approach near Yuma, flying without an airworthiness certificate, and the second flight in 2017 did not solve the underlying problem, which also stalled Zephyr: a solar airframe cannot carry a useful payload and survive the night at anything but equatorial latitudes. Loon, the balloon program, closed in January 2021 when Alphabet said no commercial case materialized (meaning the Pentagon backed out).

Inside the high walls of the Facebook campus it was like humanity didn’t matter, money-fueled madness made anything possible (e.g. Musk’s “occupy Mars” is a campaign to abolish laws and replace with an Emperor). Outside, the laws broke every power-hungry fantasy. That’s why Facebook shut the airframe program in June 2018 and said Airbus would build the aircraft instead (e.g. Tesla initially had Lotus build its cars to avoid itself having to operate within the law); and that partnership faded quietly.

Fast forward to today and Meta has announced an engineering nothing-burger.

We’re announcing Petal, the first subsea cable with petabit capacity to be deployed across an ocean. Petal will connect the US and France, spanning 7,000 km (over 4,300 miles) and doubling the capacity of today’s most advanced transoceanic cables.

The doubling isn’t surprising and comes from two-core fiber rather than more strands, which is why the announcement leans on “without proportional power or infrastructure.” That is also a concentration-of-risk claim: same number of cables, same landing points, same Baltic and Red Sea failure modes, now carrying twice as much per cut.

The constraint has been voltage, not glass. So repeaters split each 2-core fiber into two single-core paths with a fan-in/fan-out interface, amplify, then recombine, which keeps the system under the existing 18 kV power-feed rating and avoids requalifying the whole subsea ecosystem. Meta doubled capacity by staying inside the old certification envelope.

Meh. Or should I say Meh-ta?

It is obviously foremost a cable for moving Meta’s own traffic between its US and EU data centers, increasingly AI training and inference, that seeks EU exposure and dependence on American compute. Read between the lines and it is a political science post, without much technical significance, dressed up as something novel that engineers did.

Meta stopped trying to route around states and started embedding in them instead.

It plans to land in France with Orange as landing party, which puts Meta inside French critical-infrastructure policy, inside French lawful-intercept obligations, and at the table when governments talk about cable protection. That is a far more politically durable position than hoping nobody touches an aircraft too fragile to survive its landing.

Colonization by cable is probably the right way to read the news, if you consider history. Paris learned what happened in the Fashoda Crisis of 1898 from a British telegram routed through Cairo, and when Britain censored the cables during the Boer War the next year, France started building a state-owned network to Africa.

The two major colonial powers sought to link their colonies via a vast railway network: Britain from Cairo to Cape Town, and France from Dakar to Djibouti. The town of Fashoda, situated at the intersection of these two planned lines, became a critical focal point for both armies. On September 18, 1898, Marchand’s French mission and Kitchener’s British expedition came face to face on the Upper Nile. Ordered to withdraw, France yielded and was forced to acknowledge British authority over the entire Nile basin. This defeat led to a redivision of African colonies between the British and the French.

What will Meta surveill and censor for Trump when the EU goes to war?

On the current cable at Le Porge Meta holds more than 80%, Orange gets two of sixteen fiber pairs for landing it, and the ownership split is not public.

Can you guess why it’s not public? On the US side the FCC landing license for Amitié went to Microsoft, and since 2020 the FCC refers cable landing applications with foreign ownership to a Justice Department-led committee that can condition the license on a national security agreement. Whatever the licensee agreed to in Washington is part of the deal France landed.

Petal goes to NEC and Sumitomo, two years after the French state bought 80% of Alcatel Submarine Networks to keep cable building sovereign, and seven years after the Senate warned in 2019 that these infrastructures must not be held exclusively by foreign entities.

France keeps one thing. Le Monde reported in 2014 from the Snowden files that Orange’s landing stations give the DGSE access to everything transiting the country, sorted by origin.

Meta owns the cable. France owns the landing and reads it. That is the same arrangement France rejected in 1898, with the tap as consolation, and good luck to France when it remembers why.

Wheatley to Orelien: Racist Information Warfare Targets Black Authors

The Academie Goncourt struck a novel from its longlist on Friday, four days after an anonymous account with 92 followers declared it the work of a machine. The evidence was a single commercial detector. AFP ran the same passages through its own tool and got “very likely written by a human.” Seven other detectors disagreed with each other.

The book stayed struck. The Goncourt cited the plagiarism findings alongside the detector, but the claim by an anonymous account with a contested tool was clearly targeting the author.

The author is Thelyson Orelien, 38, born in Gonaives, Haiti, resident in Montreal since 2010. His first novel, C’etait ca ou mourir, follows a teacher fleeing gang violence to Canada. It won the Prix du Roman Fnac on Monday 21 September. The accusation from “Balance ton Claude” landed the same day. By Thursday his Quebec publisher had suspended promotion, a book fair had withdrawn his guest of honour title, and two newspapers had found borrowed passages in columns and a short story he wrote in 2012 and 2014. By Friday the Goncourt had acted “to preserve the integrity of the prize” and its mission of crowning “literature written by women and men.”

On Thursday Le Figaro identified the attack account’s operator as one of its own columnists, Samuel Fitoussi, author of Woke Fiction. He had denied involvement to AFP several times that week. He had also been among the first to repost the anonymous accusation from his own named account, boosting himself. On Friday he confirmed a “collective project” whose other members remain unnamed. Asked about the racial dimension, he called the question conspiracist. The president of the Academie Goncourt had already told franceinfo why he thought the timing mattered: a Haitian, Canadian, Black, francophone foreigner, in a season when passions run high.

Fitoussi’s stated motive is fear, that AI will end human writing. Yet he is an associate member of Frst, a Paris fund that finances AI startups and that began life as Otium Ventures under the Catholic billionaire Pierre-Edouard Sterin. The detector he relied on, Pangram, raised $9 million in July in a round led by Menlo Ventures, an investor in Anthropic, whose assistant gave the account its name.

Black authors in the French and English worlds have been asked to prove they wrote their own books for 250 years.

Phillis Wheatley was examined by eighteen Boston men in 1772, Governor Thomas Hutchinson among them, before a London publisher would print her poems. Their signed certificate that she had written them opens the 1773 edition. Bakary Diallo, a Senegalese rifleman, published Force-Bonte in Paris in 1926 and was assumed for decades to have had it written by his French patrons. Camara Laye’s Le Regard du roi (1954) was attributed in 2002 by the scholar Adele King to two Belgians in Paris, his landlord and a reader at his publisher. Yambo Ouologuem won the Renaudot in 1968 for Le Devoir de violence, faced plagiarism charges from 1971, and published nothing after 1972.

A white author gets the opposite treatment. Michel Houellebecq copied Wikipedia passages into La Carte et le Territoire, admitted it, called it collage, and won the 2010 Goncourt anyway.

Orelien is compiling a dossier with his editor to prove he wrote his own book, like Wheatley stood before eighteen examiners in Boston over 250 years ago.

The information warfare against Black authors hasn’t changed much.