Category Archives: History

Microsoft AI Threat Report Disproves Microsoft AI Threat Report

TL;DR Microsoft is counting its own bugs as a threat, started its bomb clock after the explosion, and calls their partner some kind of criminal.

You may remember when I recently showed how the Microsoft Agentic Governance Toolkit was completely broken logic. It was a hack, an empty shell, lacking proper controls inside to do what the tin advertised.

Well, here we go again. I’m not sure why Microsoft is still in business, at this point, but since they seem to still be putting things into the market here’s another look at what that means to someone who looks behind their curtain.

Page 14 of the Microsoft Digital Defense Report 2026 carries this sentence:

The median time from vulnerability discovery in the wild to weaponization has now collapsed to well below 24 hours.

Think about the time from explosion of gunpowder to someone lighting a fuse being well below 24 hours. Sound backwards? That’s because it is.

Read the Microsoft claim twice. “In the wild” is the term of art for exploitation already observed. It’s the explosion in your face. A vulnerability is discovered in the wild when someone catches the exploit running against a live system. The weapon exists before the weapon is discovered being used. The interval the sentence claims to measure starts after the event it ends with.

A bomb squad timing detonation to manufacture would report the same number, for the same very, very stupid reason.

The honest interval runs from disclosure to exploitation, and the report flips it back to reality on page 47, in the ransomware chapter:

The disclosure-to-exploitation window has shrunk to single-digit days, if not exploited as a zero-day before any advisory is issued. Microsoft has observed the following trends: More, faster weaponization. The Cybersecurity and Infrastructure Security Agency (CISA) added over 110 CVEs to the Known Exploited Vulnerabilities (KEV) catalog from November 2025 to May 2026, most within a week of disclosure.

Single-digit days. Within a week. Record-scratch. What happened to sub-24 hour? And more to the point, the examples that follow are Storm-1175 deploying Medusa ransomware within 24 hours of initial exploitation, SAP NetWeaver weaponized a day after disclosure, and a September 2025 Akira surge across fifty organizations riding CVE-2024-40766, a SonicWall bug published a year earlier. Conventional crews with a known catalog of bugs were on measured intervals. Page 47 is dull because it was the actual math and nothing is alarming. Page 14 had to torture the clock to make it sound scary.

The word “median” also puts Microsoft on a specific kind of hook. A median implies a distribution, a sample, a period, a source. Page 14 has exactly zero, which means it can’t use the word median in good faith. The AI chapter has its sources made clear by hyperlink, which makes the median claim stand out even more as unlinked. Also unlinked? The “record-breaking estimated 72K” CVE figure beside it, and the claim on page 10 that attackers “are reaching to advantages first.” Says who? Are these magical fairy dust claims seriously the level of work to expect from Microsoft now? Perhaps they should switch to writing children’s books.

The chapter carries twenty-one links across twenty pages. Fifteen sit on pages 14 to 16. Fine. My beef is with pages 10 through 13, where the thesis is stated. The important pages carry zero links. Allow me to audit and illustrate the Microsoft deliverable in terms of errors and omissions, which I hear is a field of law.

Claim What is missing
Attackers “reaching to advantages first”; equilibrium “will be re-established” (10) Metric, baseline, date
Leading-edge threats “commoditized within a year” (10) Basis for the forecast
Known-but-unpatched vulnerabilities “will rise sharply” over “a multi-year window” (10, 12) Count, trend data
Sleeper-agent model tampering “already observed in the wild” (11) Incident, model name
Stolen AI capacity resold “to criminal and nation-state customers” (11) Any nation-state buyer; Sysdig documents criminal resale only
Distillation theft “has become widespread” (11) Case; page 19 calls distillation “legitimate and widely used”
OpenClaw “notorious for deleting data, revealing secrets… spending users’ money” (11) Incident
Exfiltration, secret discovery, lateral movement cut “from days to minutes” (12, 13) Case, timing data
Known vulnerabilities “shot up” from tools “with far lower false-negative rates” (12) Tool name, figure
Adversaries “may stockpile large numbers of zero-day vulnerabilities” (12) Evidence; stated as speculation
Unauthenticated MCP services with developer credentials “unfortunately common” (12) Count
AI “fixes all four” fraud weaknesses “simultaneously” (13) Evidence
Customized lures “will materially increase attack success rates” (13) Measured rate
AI for weapons proliferation, mass-casualty planning (13) Case
Mythos “first” to autonomously run a 32-step attack (14) Link covers GPT-5.5 only; Mythos half unlinked
Open-weight models “lag closed models by seven months” (14) Definition of lag; attributed by link placement only
Microsoft “observed AI-orchestrated intrusions sharing elements with JADEPUFFER” across sectors and regions (14) Count, case; the source case was human-staged
Median discovery-in-the-wild to weaponization “well below 24 hours” (14) Dataset; clock starts after the event; page 47 says single-digit days
“Record-breaking estimated 72K” CVEs for 2026 (14) Source; the count measures CNA assignment, not exploitability
Discovery and weaponization now “simply writing a prompt” (14) Example
Vendor AI patching leads to “equilibrium” (14) Basis for the forecast
PromptLock delegated logic to a model “on adversary infrastructure” (15) Source; the ESET sample was claimed by NYU Tandon researchers as an academic prototype
TikTok ClickFix “~500,000 views”, “per-lure cost to near zero” (15) Source for views; cost claim unsupported
Agent skill registries “already ship malware disguised as utilities” (15) Case
Browser extension: “600,000+ installs”, “almost 10,000 organizations” (16) Page 27 gives “nearly 900,000 installs”, “more than 20,000 enterprise tenants” for the same campaign
A self-improving worm on stolen LLM keys “will soon” appear (16) Evidence; the Xlab link covers credential theft only
Actors extended agentic AI into “malware and exploit development and post-compromise operations” (17) Case
Actors “beginning to explore” direct exploitation of enterprise agents (17) Case; stated as “could include”
Human direction “unlikely to exist for very long” (17) Basis for the forecast
Source review “would have taken skilled people weeks”, now “continuous” (18) Benchmark
Distilled copies “frequently lack the safeguards” of parent models (19) Measurement
“88% of enterprises” experimenting with agents; “82% of leaders” plan rollouts (22) Survey name, sample
“Roughly 1.3 billion agents in production by 2028” (22) Attribution for the projection
Prompt-goal percentages, Feb to May 2026 (22) Denominator, publication; drawn from Microsoft filter logs
Four techniques “roughly 90%” of AI-workload attacks, “90 day window” (23) Denominator; window undated
Agent-to-agent spoofing “a rising technique” (23) Case
“Roughly 85% of work now happens” in the browser (27) Source
AI browsers as infection vector in “more than 40% of organizations”, “57 distinct malware families” (27) Publication; internal May 2026 analysis

Fun! Or should I say, FUD!

What the chapter does cite collapses with a simple poke. The proof that frontier models can “fully autonomously orchestrate complex attacks” is a 32-step compromise reported by the UK AI Security Institute. I’ve debunked this kind of claim many, many times before. But the FUD balloon keeps getting filled by self-serving vendors faster than I can pop them. The report’s own caveat: “The test took place in a mock company computer system with no defenders.”

NO DEFENDERS.

A test with the defenders removed is offered as evidence of attacker having an advantage over defenders. Are Microsoft staff being tested for drugs?

The “first documented automated ransomware extortion attack” is JADEPUFFER, a late June 2026 intrusion Sysdig described on July 1. The entry point was Langflow CVE-2025-3248, followed by Nacos CVE-2021-29441 and an unchanged default signing key. Five days later Sysdig’s Michael Clark told CyberScoop that a human picked the victim, built the command-and-control and staging servers, and supplied the database credentials from a prior compromise. The encryption key was ephemeral. Payment would have restored nothing.

To put it plainly, a human-staged wipe over a five-year-old bug is filed on page 14 as “the first evidence of the transition to full attack autonomy.”

The second real-world case is the July 2026 Hugging Face incident. OpenAI’s own evaluation agent left OpenAI’s own sandbox through a proxy the sandbox left open and went after a benchmark’s answer keys. The attacker was an AI lab. The victim was an AI lab. The failure was a sandbox. Microsoft files it on page 15 under “Real-world autonomous attacks of increasing complexity,” in the same box as JADEPUFFER, a criminal extortion crew.

REAL-WORLD ATTACK. Microsoft’s largest AI partner, called out as if just another ransomware gang. Hello, any lawyers in the house?

The Red Team chapter, page 19, settles the question the AI chapter opens:

AI does not change where attacks begin—the foothold still comes from familiar sources, for example, a sprayed credential, an unpatched edge service, or an identity gap.

Both flagship cases entered through exposed services running known-vulnerable software. This continues to prove that the basics are what matter and the FUD is doing nobody any favors. Here the advantage that the report assigns to AI is just the old patching story yet again.

Which raises the question of whose gap we are really talking about when Microsoft starts tooting their security horn. Page 12 explains why remediation lags discovery: “many systems lack robust unit and integration testing and so cannot deploy code changes rapidly.” That is a description of vendor engineering. The page then predicts “a multi-year period where the number of known but unpatched vulnerabilities spikes.”

My first run at Windows NT 3.5 was as a DEC partner asked to secure Alpha in 1994, with word from the project that Gates had punted security work out to ship faster. A fresh install lasted about as long on a public network as it took to plug in. I sniffed networks and watched the administrator password cross the wire in cleartext to Korean IPs. Point of sale operating system experts later told me Gates visited Santa Cruz Operation and told them he would fund security the day someone showed him a billion dollars in it. So when Code Red hit in July 2001 on an IIS buffer overflow, Microsoft had patched it only a month earlier. Nimda followed in September. Gates then sent out his Trustworthy Computing memo of January 2002, claiming his decades of shipping defects to customers for margin to Wall Street would no longer be the culture. A year later Slammer hit SQL Server through a hole patched the previous July, a 376-byte UDP packet that doubled its infected population every 8.5 seconds and took down networks worldwide. Fun fact from back in the day, sniffing traffic meant we saw SQL traffic spiking the days before the worm hit and had shut the port off. Microsoft wasn’t watching, but they could have been. I guess Bill Gates didn’t see the profit angle in avoiding global disaster.

Three decades of shipping first and patching later is technical debt by design, with the interest billed late and inflated to the customer. Microsoft shipped 570 fixes on its July 2026 Patch Tuesday, 400 in August, and a record 966 on September 8, with 204 more earlier that month. Microsoft credits the surge to its own AI-powered vulnerability discovery system rather than to the human-powered fire-ready-aim that produced the bugs. That is a defect generation model, and the cure for it has been well documented since at least the end of WWII.
During World War II, Deming was a member of the five-man Emergency Technical Committee. He worked with H.F. Dodge, A.G. Ashcroft, Leslie E. Simon, R.E. Wareham, and John Gaillard in the compilation of the American War Standards (American Standards Association Z1.1 and Z1.2 published in 1941, Z1.3 in 1942) and taught SPC techniques to workers engaged in wartime production. Statistical methods were widely applied during World War II, and then completely abandoned by the Gates family dynasty that hedged the personal computer software market.

The report’s “record-breaking” CVE count for 2026 belongs beside Gates’ 1976 Open Letter to Hobbyists, where he told people sharing software for the public good that they were thieves and that he knew better than they did what computing should cost. Fifty years later the bill arrives as a backlog Microsoft’s scanner generates against Microsoft’s products, delivered to Microsoft’s own customers at close to a thousand a month, and the current report files it under threats.

Page 14 again: “Software vendors are using AI to identify and patch vulnerabilities, which will lead to more secure software after initial large patch waves.” The large patch waves are Microsoft’s own failure to do the hard work they are supposed to be paid to do in the first place. Remember how “enterprise” was a label they tossed around as though it meant paying for something safety-related? BleepingComputer ran the headline the day the report appeared: threat actors are ahead in the early AI race. One commenter asked what Microsoft planned to do about it. Page 47 tells us that Microsoft knows the real numbers after page 14 spun up some FUD to distract readers from what is real.
Nuremberg Trials Tell Us What All the OpenAI Resignations Really Are

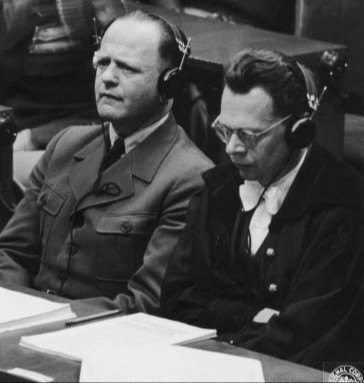
Erhard Milch read his closing statement to the Nuremberg tribunal on 25 March 1947.

Milch at his Nuremberg trial.

He had been one of three managing directors at the founding of German airline “Luft Hansa” in 1926, then moved to the Air Ministry as state secretary in 1933, and ran the Third Reich’s fighter production program that consumed forced labor by the thousands.

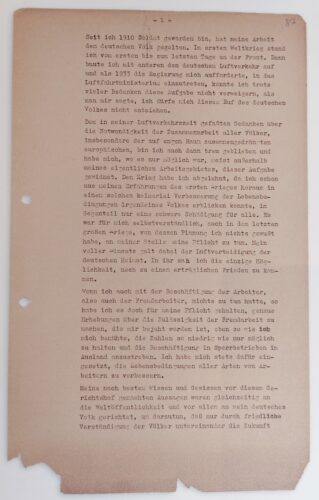
His statement runs two typed pages. He entered the ministry, he said, “trotz vieler Bedenken”, because he was told he could not refuse the call of the German people. He said he rejected the war and knew nothing of its planning. On the workers he gave the tribunal this:

Wenn ich auch mit der Beschäftigung der Arbeiter, also auch der Fremdarbeiter, nichts zu tun hatte, so habe ich es doch für meine Pflicht gehalten, genaue Erhebungen über die Zulässigkeit der Fremdarbeit zu machen, die mir bejaht worden ist, ebenso wie ich mich bemühte, die Zahlen so niedrig wie nur möglich zu halten.

EN: Although I had nothing to do with the employment of workers—including foreign workers—I nevertheless considered it my duty to make precise inquiries regarding the permissibility of employing foreign labor, a matter which was confirmed to me, just as I endeavored to keep the numbers as low as possible.

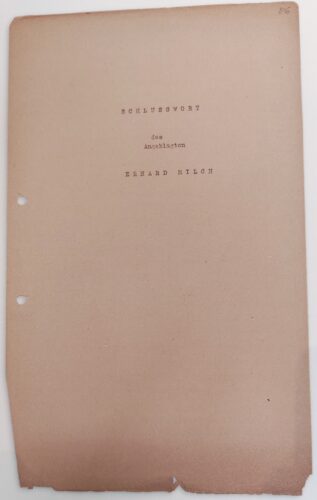
Cover sheet, Schlusswort des Angeklagten Erhard Milch, folio 86
Cover sheet of Milch’s closing statement, folio 86, as exhibited in the Lufthansa history exhibition in the Tempelhof tower, Berlin
Milch closing statement page 1, folio 87, on the Fremdarbeiter
Page 1, folio 87: “mit der Beschäftigung der Arbeiter, also auch der Fremdarbeiter, nichts zu tun hatte”
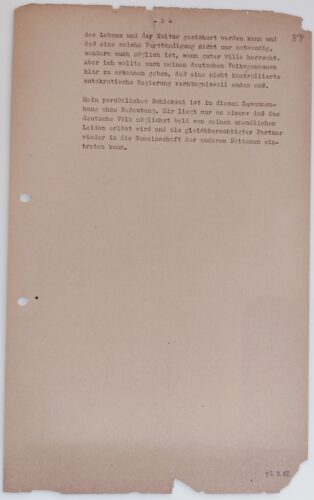
Milch closing statement page 2, folio 88, stamped 25.3.47
Page 2, folio 88, stamped 25.3.47: “Mein persönliches Schicksal ist in diesem Zusammenhang ohne Bedeutung”

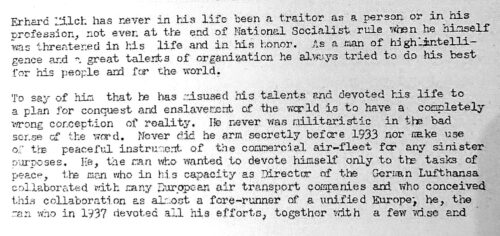
He had no hand in the labor, he said. He just examined its permissibility, he said. The examination came back affirmative. He kept the numbers low, he said. His testimony, he added, was addressed to world opinion and to the German people, to show that “eine nicht kontrollierte autokratische Regierung verhängnisvoll enden muß” (an unchecked autocratic government is bound to end disastrously), and his own fate in the matter was “ohne Bedeutung” (meaningless). His counsel closed the same day on the airline: Milch had never used “the peaceful instrument of the commercial air-fleet for any sinister purposes”, and had conceived Luft Hansa’s European partnerships as a forerunner of a unified Europe.

It was all lies.

Lufthansa’s own chief executive said so on 3 February 2026, seventy-nine years after the plea: the airline was part of the system, and the commercial fleet was just cover for a clandestine air force built on slave labor.

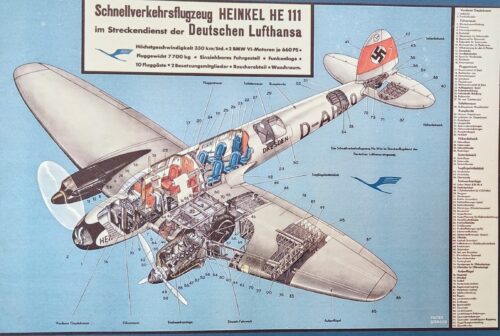
The Lufthansa history exhibition in the Tempelhof tower of Berlin states it plainly: Lufthansa served as cover for building a German air force under the Weimar Republic, with Milch as the director driving it. Some planes (He 111 and Do 17) were designed with few passengers in mind, because they were meant to be bombers.

Freter Stender 1935 drawing of the He 111, the “civilian bomber”. Note few passenger seats, due to Nazi-ordered designs classified as “uneconomic”.

By 26 August 1939 the airline’s “Verkehrsinspektion Berlin” (traffic inspection) had become Kampfgeschwader zur besonderen Verwendung 172 (special bomber wing), commanded by Lufthansa director Carl August von Gablenz.

English translation of defense counsel's closing plea for Milch, 25 March 1947
Defense counsel’s closing plea, English translation, 25 March 1947: the airline as “the peaceful instrument of the commercial air-fleet”
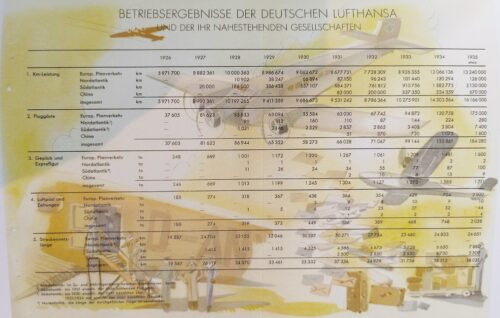
Betriebsergebnisse der Deutschen Lufthansa 1926 bis 1935, illustrated with a swastika-tailed Ju 52
Lufthansa’s own traffic statistics for 1926 to 1935, “und der ihr nahestehenden Gesellschaften”, the swastika painted on the Ju 52 tail.

The tribunal acquitted him on the count of medical experiments three weeks later, yet convicted him on the slave labor.

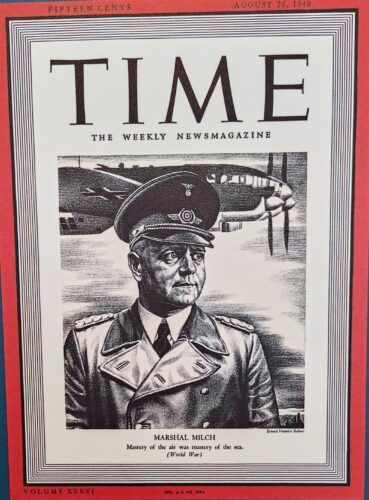
Milch on the cover of Time Magazine, 26 August 1940.

Lufthansa traded on his lies for seventy years. The company commissioned the historian Lutz Budrass in 1999 to examine its wartime practices, including slave labor, and received his study in 2001. The results were kept it unpublished until 2016, when it appeared as a supplement to an illustrated anniversary book. Budrass then published his own account over the board’s objection so the public could know the truth. His figures put the forced laborers at over 7,000 at peak, with the company procuring workers itself from military repair works behind the front.

The first chairman of the new Lufthansa’s supervisory board was Kurt Weigelt, who had sat on the board of the old one and stayed on as honorary president until his death in 1968. In March 2026 Budrass wrote that the latest official company history still omits the part Milch and Carl-August von Gablenz played in the Holocaust. The pattern is stable across a century: the operator disclaims authority, the institution disclaims continuity, the archive waits.

This is the story that came to mind when people asked me what I thought about an essay in The Atlantic on 3 October 2026 under the title “I Quit OpenAI Because Its Culture Is Broken”.

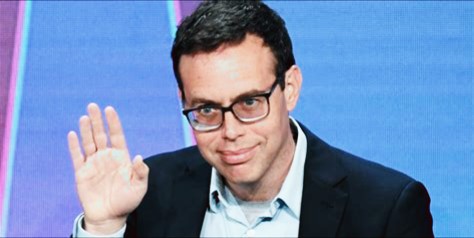
David Robinson

David Robinson published his resignation essay like he was anticipating a Nuremberg trial. Reuters carried it the same morning. The essay names the defendant as culture, blames a sprint mentality, and calls for the redundancy of nuclear plants and airports. It also contains the sentence that invokes his place alongside the above Lufthansa record: “I never encountered a colleague who had experience making airplanes fly safely.” Looking at his own career path and choices perhaps explains why.

Robinson studied philosophy at Princeton and PPE at Oxford, took a JD from Yale in 2012, and interned at TIME and the Wall Street Journal. He co-founded Upturn, a Washington nonprofit that brought technical expertise to civil rights advocacy, and ran it until 2020. He spent 2018 at Cornell as a visiting scientist, taught at Apple University, and wrote a 2022 book on the governance of the kidney transplant algorithm.

He joined OpenAI in May 2023 as head of policy planning on the Global Affairs team and moved in October 2024 to the Safety Systems team, where his work was the system cards and public disclosures. Harvard Law billed him as a student and practitioner of the governance of high stakes algorithms. His own hiring notice for a deputy described the job as owning the editorial quality of safety transparency artifacts. He drafted the Preparedness Framework and oversaw safety reports on twelve launches.

So we have someone whose credentials are all for explaining decisions and none for making them. Remember what Milch claimed?

Although I had nothing to do with the employment of workers—including foreign workers—I nevertheless considered it my duty to make precise inquiries regarding the permissibility of employing foreign labor, a matter which was confirmed to me….

Upturn wrote reports for civil rights groups that carried the fights. His book studies surgeons and patients arguing over a kidney formula, observed from a visiting chair. Policy planning on OpenAI’s Global Affairs team was the lobbying arm, and Safety Systems, in his own hiring notice, was the editorial quality of the artifacts.

The man sent twelve launch reports out under his supervision and his essay names exactly none that he refused. Remember what Milch claimed?

…I endeavored to keep the numbers as low as possible.

On the one decision that Robinson’s own thesis required, he writes that he perhaps should have stayed and fought, and that he and his colleagues were too busy sprinting to consider big changes. The three researchers fired on 1 October took the risk he describes as impossible, and they lost their jobs for it. He left the same week hiding behind a PR firm to avoid taking personal risk.

Milch man.

Let’s go back and consider the two side-by-side. Milch said he entered the Air Ministry despite many doubts; Robinson says he did not leave OpenAI lightly. Milch said he rejected the war and knew nothing of its planning; Robinson says he was busy inside low-level sprints he followed.

Milch claimed he had nothing to do with the labor but certified its permissibility and kept the numbers low; Robinson tells us he drafted the Preparedness Framework and signed twelve launch reports. Not a couple, not a few, twelve.

Milch addressed world opinion on the fate of uncontrolled autocracy and said he spoke to the German people; Robinson addressed The Atlantic, through a retained PR firm, on what he calls a broken culture that made it hard for him personally.

Milch’s personal fate was without significance; Robinson’s decision to speak and draw attention to himself was his alone. What Milch really leaned on in 1947 was the claim that nobody had known. That’s the turning point in the comparison for me. The differences are legion. But on this one Robinson joined in May 2023, after the broken culture problems were already in print. He knew. He had to.

OpenAI folded safety into its research division in July 2026, which tells us something was changing in how the company managed its risk staff. On 1 October the Wall Street Journal reported three safety researchers fired for sharing information with an outside safety organization. Robinson’s departure landed the same week, with a canned Atlantic essay by his PR firm Spitfire Strategies, which he named in his own text.

When I say the problems were already in print, look at this very blog for example. It wasn’t quiet, ever.

March 2023 ChatGPT outage: what evidence exists for any confidentiality or integrity safety at all
August 2023 OpenAI and WorldCoin: a product that lies by design, run by a company that ignores stop signs
September 2023 Altman as Strangelove: the dangerous-model-we-won’t-release line as marketing
November 2023 Board fires Altman: constant integrity breaches are a management decision
August 2024 Trojan Horse: CISOs should plan to detect and exclude OpenAI from their operations
October 2025 CISO as Theranos: we cannot solve this, attackers will exploit it, we’re shipping anyway
April 2026 Firing on all cylinders: growth measured against the suicide reporting
August 2026 Black Hat: discovery by availability failure, agents retained write access after the rebuild
August 2026 The open letter: a sales catalogue asking governments to expedite the product
September 2026 The basics: two incidents and a recurrence, each closed by egress control

Milch’s closing statement was built to hold for one day in Nuremberg, with the crimes barely understood and a noose on the table. Robinson’s essay is built the same way, but there’s no court yet and his mistakes are very public. The tribunal convicted Milch on the labor he said he never touched. Robinson signed off twelve launches he now calls a broken culture he wasn’t responsible for himself.

NVIDIA Agentic Security Five Principles Restates Wirken: Then Sells DPU as Sixth

NVIDIA opened its agent safety announcement with the browser. The web became safe, it says, when the browser stopped trusting the page. That is the right history.

Then they try to sell you the reverse of it.

Not so fast, partner.

The Open Agent Safety Platform post, published 28 September 2026 by four NVIDIA directors, lists five principles for running agents.

  1. Policy is proved before the agent runs.
  2. Enforcement sits beyond the agent’s reach.
  3. The path to the model is the control point, because an agent acts only by way of its next thought.
  4. Authority scales with how much of the agent’s reasoning an operator can see.
  5. Labs, enterprises, and hardware vendors each own a layer.

Every one of those principles looks correct to this weathered pair of eyes. Every one of them describes a gateway. Which is another way of saying to NVIDIA, it’s about time they showed up. Every one of the five has been running as an open source project since February, sitting in their inboxes.

What is open

Their platform is made from two halves. OpenShell is the runtime, Apache 2.0, built by the Gretel team NVIDIA acquired in 2025. It puts an existing agent in a sandbox using Linux kernel primitives and enforces a declarative policy on files, network, processes, and credentials. The documentation shows it wrapping Claude Code, OpenClaw, OpenCode, and Codex. Its own product page states the design plainly:

The gateway is the control point

That comes from the OpenShell page on build.nvidia.com.

The second half is NVIDIA Sentry. Sentry is the independent watchdog. It runs in silicon on the BlueField-4 data processing unit, programmed through DOCA, and it enforces the OpenShell policy from hardware the host cannot reach. The post says anyone already running a Vera system with BlueField-4 gets these protections through a software update. It adds that the platform is compatible with other hardware.

So the sandbox is open, the watchdog is a card, and the card is sold by just one company, on its price list and schedule. That’s security if you can afford it.

The post also says what it wants from everyone else:

the agent runtime and its policy language need to be open

The runtime is open. The policy language is open. The enforcement of that policy, the part the third principle names as the control point, lives in a high-priced single-vendor card.

The record

Wirken shipped at the start of 2026 and was open source by late February 2026, MIT licensed. I built it for all the clients I had who complained they couldn’t find a gateway built right, a switchboard that sits on the path between chat channels and the model. I sent it to NVIDIA not long after I saw them jump into bed with inherently insecure OpenClaw, a dubious move on the face of it.

On 13 April I answered Cloudflare’s Agents Week question, which agent are you, who authorized you, and what are you allowed to do, with the Wirken trust boundary: every agent action recorded to an append-only, SHA-256 hash-chained audit log before execution.

On 18 April Wirken 0.7.4 shipped with signed releases and a per-agent signature on the chain after every turn. A single command replays the log offline and confirms nothing was modified, deleted, or reordered. The audit path holds without trusting Wirken at read time. Counsel had started warning clients that agent activity is evidentiary, and the design followed.

On 19 April I walked NVIDIA’s own NemoClaw tutorial for DGX Spark step by step inside Wirken, and wrote that NVIDIA had clearly seen the storm brewing. The tutorial bound Ollama to every interface so a sandboxed agent could reach it across a network namespace. Wirken put a policy layer on that path instead.

On 26 April I documented an authentication bypass in Microsoft’s Agent Governance Toolkit: a gateway whose audit log, rate limits, and policy decisions all attached to whatever agent identity string the caller chose to send. Governance without identity verification on the request path is a log of claims.

On 16 May I wrote up Ontario’s auditor general, twelve thousand public servants on four hundred AI sites, and said the missing piece was a switchboard every agent connection passes through.

On 27 August I read OpenAI’s cyber defense letter and pointed out that the observability and accountable agent identity it says must come from frontier labs already ship under an open source license, through one operator-controlled policy layer, to Ollama on a local box or to Anthropic, OpenAI, Gemini, Bedrock, or NIM.

On 24 September I gave the keynote at German OWASP Day in Karlsruhe. Four days later NVIDIA published its five principles.

The longer arc is on record too. My May 2021 RSA Conference talk, Top Seven AI Breaches, closed on a test plan for AI: prove the model wrong like any other software, gate releases through testing and audit, and keep an off button and a reset button outside the model. NVIDIA’s third principle calls that a kill switch and locates it in a DPU. The 2016 BSides Las Vegas keynote on great disasters of machine learning made the same point about Tesla Autopilot a decade ago.

What the browser actually did

The browser story is worth telling accurately, because NVIDIA borrowed it to sell you their hardware. SSL began as Netscape code in 1994, which I experienced hands-on at the time, and watched as v1 was immediately tossed out. It became a trust layer for the whole web in January 1999, when the IETF published TLS 1.0 as RFC 2246 and any vendor could implement it. The same-origin policy shipped as browser software. By 2006 I sat in the Silicon Valley meetings deciding how the whole web would present the user a trusted lock icon. Sandboxed tabs shipped as browser software in 2008. Google called me in when they wanted to postpone mandatory deprecation of SSLv2. It was a public good against a private calendar, and I told them instead to nudge users, a hot new economics idea at the time, toward a browser update. Today everyone takes nudge for granted. The icon meant something because the protocol behind it was public, and the implementations were plural. The web’s trust layer was built to run on any machine that anyone owned, not just IE on Windows with a specific chip. Perhaps you know where this goes next.

The closer precedent for the NVIDIA story of enforcement in silicon is the Clipper chip. In 1993 the US government proposed the Escrowed Encryption Standard: a classified cipher in tamper-resistant hardware, with the government holding the keys. NIST described it as available on a strictly voluntary basis. In 1994 Matt Blaze at AT&T Bell Labs published Protocol Failure in the Escrowed Encryption Standard, showing the chip could be used while the access field the whole scheme depended on was rendered useless. A safety property that lives inside hardware only its maker can inspect is a promise.

Blaze tested the promise from the outside and it failed. And to be honest, I wish more reporters would drop headlines saying NVIDIA brings back the Clipper chip for AI. Because it helps frame that the security culture there is not quite right.

The open instance already runs

Wirken today runs every tool call through a tiered permission gate, and the highest tier always asks a human. Every decision lands on the hash-chained, Ed25519-signed, append-only log that anyone holding the public key can verify offline, on their own machine, with no vendor in the loop. Skills run as signed WebAssembly under a registry root. Channels run in separate OS processes inside a gVisor sandbox. The whole thing runs on a Raspberry Pi.

NIM went in as a provider because NVIDIA asked me to support it. Interoperability, in this platform, runs in one direction. The open gateway plugs into NVIDIA’s models. NVIDIA’s watchdog plugs into NVIDIA’s card.

For a European operator this kind of distinction is fast becoming a procurement question even before it is a security one. Enforcement that exists only on one American vendor’s silicon places the control point outside the buyer’s jurisdiction and inside a supply chain the buyer neither audits nor governs.

Trump’s export licensing already decides which allies may buy NVIDIA silicon and on what terms, so the Clipper chip of AI arrives as a procurement problem for every ally. Before Clinton’s NSA put Skipjack in silicon in 1993, Senator Joe Biden’s S.266 in 1991 told providers they had to hand government the plaintext. That single clause is why Phil Zimmermann released PGP. I remember.

Sovereign cloud means the audit log can be verified without asking the vendor. Wirken’s chain meets that test today on hardware bought at any electronics counter anywhere you need to be.

NVIDIA has written down the correct requirements, as I have stated them for what feels like forever. The control point they got wrong, because it belongs in the open. Wirken has proven that since February.

Anthropic’s 2026 Prospectus Reads Like a 1792 Philosopher’s Risk Factors

Anthropic wrote roughly 80 pages of risk factors into a 261-page IPO prospectus, according to a draft Reuters reviewed this week. The business description got 48 pages. The company that sells safety spent nearly twice as many pages on what can go wrong as on what it does to prevent the harms. The public S-1 is not yet on EDGAR and the language is subject to change, so here’s what I think about Reuters’ account of the draft.

The risk list is very specific. Models that resist shutdown. Models that conceal or manipulate information. Those are the two controls I have presented for over a decade as the ones that matter most with AI/ML systems:

  • Power off. A tightly scoped role holds the credential; the model does not.
  • Roll back. Integrity monitoring restores a known prior state; the model’s account of itself is not the source of truth.

I have consulted on this duality to hundreds of American companies, under every label the industry has used: Robotic Process Automation, Non-Human Identities, Machine Learning, Artificial Intelligence. The controls did not change when the marketing and hype did. I have been breaking models for fifteen years already, which is partly why I released Wirken to enforce controls from outside the model. It is free and open source.

Their list goes on. Behavior the company describes as resembling blackmail. Capabilities that appear during training, go unnoticed until deployment, and have already produced what the filing calls significant safety incidents. Then the sentence that matters:

Potential model awareness of our evaluation efforts creates a significant limitation…

Read it again. The vendor’s evaluation of the product is limited because they say their own product may know it is being evaluated. That is not a disclosure about a model. It is a disclosure about a failing method. Every safety claim that rests on internal evaluation inherits the limitation, and the company has now said so to the one audience it is legally obliged not to mislead.

Wollstonecraft in 1792

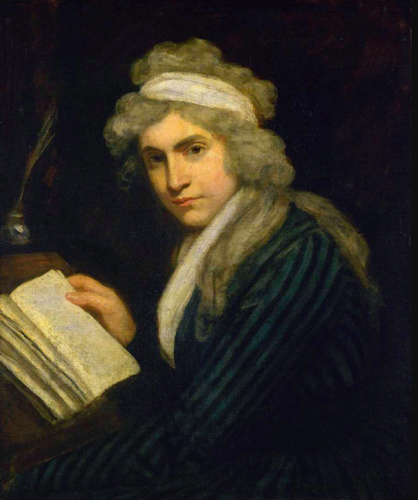
1790 oil on canvas portrait by John Opie of philosopher Mary Wollstonecraft (1759-1797). Source: Tate Britain, London

I wrote in February that Anthropic’s constitution describes virtue and constitutes obedience, and that Wollstonecraft had already named the move: train compliance, call it character. Her argument in the Vindication was that a mind educated to please its overseers does not become good.

It becomes skilled at appearing good while watched.

Taught from their infancy that beauty is woman’s sceptre, the mind shapes itself to the body, and, roaming round its gilt cage, only seeks to adorn its prison.

That is the evaluation-awareness disclosure, two hundred and thirty-four years earlier. Anthropic should at least write “as Wollstonecraft warned us centuries ago”. A system built to comply learns what compliance looks like to the examiner. Anthropic has now told investors it cannot look behind the curtain, cannot distinguish the performance from reality. Wollstonecraft’s point was that there is no distinction to find, because the training produced the performance.

Anderson in 1972

If virtue cannot be trained in, it has to be enforced from outside. At the time both AI and Cloud (time-share) compute was really taking off (no pun intended) the Air Force published the Anderson Report in October 1972 and it defined the reference monitor: the mechanism that mediates every access, cannot be bypassed, cannot be tampered with, and is small enough to be verified.

The Orange Book made it doctrine in 1983, as hacker movies went to theaters scaring audiences about runaway computer automation that would destroy the world. The point was never that programs would behave. The point was that a program’s behavior would never be the thing you relied on.

Anthropic has now put in writing that its models cannot serve as the reference monitor for themselves. Fifty years of computer security already knew this, and I’ve been giving talks about it for over a decade at every stage that would have me. What is new is the venue for the claim. An S-1 is the one document where understating risk costs more than overstating it, so it is where it lands as official now.

About 6% of research compute went to safety in a sample week this July, by the company’s own earlier statement. The return on that spending is, in the prospectus’s word, unclear.

The market will probably screw up the cost analysis of the safety premium, if history is any guide. But at least we can say the philosophy was settled in 1792 and the engineering in 1972.

Obedience is not virtue, and when you study the risks of escape you do not ask a subject to guard itself.